Yesterday the TSA published two information collection request revision 60-day notices in the Federal Register (86 FR 34775-34777 and 86 FR 34777-34778) for two pipeline security related ICRs. These are the same two ICRs for which OMB’s Office of Information and Regulatory Affairs approved emergency ICRs for increased cybersecurity reporting requirements in the TSA’s Pipeline Cybersecurity Directive back in late May. The submission of yesterday’s ICR change notices was mandated by OIRA as part of that earlier approval.
Critical Facility Information ICR
In this notice TSA provides an updated burden estimate that includes the new Pipeline Cybersecurity Self-Assessment form. The revised burden estimate is shown in the table below, the only change from the emergency approval ICR is the additional data for the PCSA.
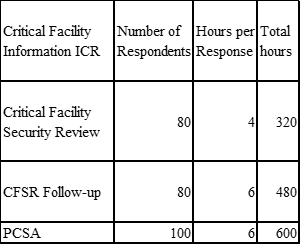
The OIRA site for the current ICR provides a link for the CFSR form currently being used under the emergency approval. It is the same form that has been used since the last regular approval of this ICR in December 2017.
There is no link provided for the PCSA form, apparently TSA never submitted a copy of that form to OIRA for the emergency approval back in May. Without access to the form, it is impossible to evaluate the amount of time that TSA estimates that it will take to complete the form. TSA should be required to re-submit this 60-day ICR revision notice after making that form publicly available for review.
TSA is soliciting public comments on this ICR revision notice. As is usual for the TSA, they do not us the Federal eRulemaking Portal (www.Regulations.gov) site for comment submission. They require that comments be emailed (or delivered) to TSAPRA@dhs.gov. Comments should be submitted by August 30th, 2021. A copy of this article will be submitted as a comment on this ICR notice.
Pipeline Operator Security Information ICR
In this notice TSA provides an updated burden estimate that includes both the new mandatory cybersecurity incident reporting and the new security point-of-contact information reporting requirement. The revised burden estimate is shown in the table below. Neither of the new reporting requirements were included in the emergency approval of revised ICR in May. There was no change to the ‘Other Incident’ reporting burden estimate.
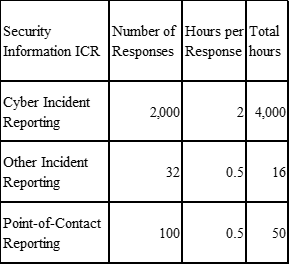
This table is slightly different from the one above in that the second column addresses ‘Number of Responses’ rather than the ‘Number of Respondents’ in the earlier table. TSA is estimating that each of the 100 covered facilities will be reporting 20 incidents per year. No information is provided for how TSA came up with that number of incidents.
The ICR Notice provides a description of the types of incidents that would be included in the voluntary ‘Other Incident Reporting’ that has long been included in this ICR. No such description is provided for the mandatory cybersecurity reporting. We have to look to the recent Pipeline Cybersecurity Directive for that information. As I noted in a separate article, the description of what would be included in a reportable cyber incident is quite expansive. I suspect that if facilities are aggressive in their reporting, that the number of incidents will be significantly larger than 20 incidents per year per facility. Lacking TSA justification for the figure provided in this ICR Notice I am forced to conclude that TSA is under reporting the potential burden.
TSA is soliciting public comments on this ICR revision notice. As is usual for the TSA, they do not us the Federal eRulemaking Portal (www.Regulations.gov) site for comment submission. They require that comments be emailed (or delivered) to TSAPRA@dhs.gov. Comments should be submitted by August 30th, 2021. A copy of this article will be submitted as a comment on this ICR notice.